


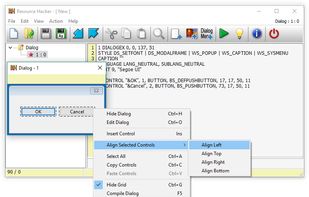
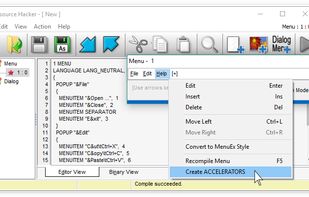
Resource Hacker™ is a resource editor for 32bit and 64bit Windows® applications.
Cost / License
- Free
- Proprietary
Application type
Platforms
- Windows
 Australia



+6


PE Explorer has been discontinued. Similar apps include Resource Hacker, which is free. Other options are HxD, 010 Editor, Malcat and Explorer Suite. Hex Editors like PE Explorer are a crowded field, with more than 50 alternatives for Windows, Linux, Mac and Android.
Resource Hacker™ is a resource editor for 32bit and 64bit Windows® applications.
Australia
HxD is a carefully designed and fast hex editor which, additionally to raw disk editing and modifying of main memory (RAM), handles files of any size.
 Germany
 EU


010 Editor is a professional text/hex editor designed to edit any file, drive, or process on your machine. Using Binary Templates technology, 010 Editor allows a binary file to be parsed into a data structure that can be understood.
 United States


Malcat is a feature-rich hexadecimal editor / disassembler / decompiler for reverse engineers and malware analysts. It has support for many file formats and CPUs, can scan for signatures, decrypt/decompress data, diff files and run python scripts.
 FranceEU


Created by Daniel Pistelli, a freeware suite of tools including a PE editor called CFF Explorer and a process viewer. The PE editor has full support for PE32/64. Special fields description and modification (.
 ItalyEU


 PolandEU


Dependency Walker is a free utility that extracts a hierarchal tree of dependencies from any 32- or 64-bit Windows executable module (EXE, DLL, OCX, SYS, DRV, etc.), including those that were built for Windows CE.
United States


Dependencies is a rewrite of the legacy software Dependency Walker which was shipped along Windows SDKs, but whose development stopped around 2006. Dependencies can help Windows developers troubleshooting their dll load dependencies issues.
FranceEU


Universal Extractor 2 is an unofficial updated and extended version of the original UniExtract by Jared Breland. It brings several hundred changes including community-wanted ones such as a batch mode, auto-updater and scan-only-functionality.
GermanyEU


Relyze is an interactive software reverse engineering and analysis platform with the following main features:
 IrelandEU


It reads and displays executable file properties and structure. It is compatible with PE32 (Portable Executable), PE32+ (64bit), NE (Windows 3.x New Executable) and VxD (Windows 9x Virtual Device Driver) file types. .NET executables are supported too.
 CzechiaEU


Hex Editor. Support editing or comparing (diff) very large files up to 2^64 bytes. Cross-platform Linux, Mac OS, Windows.
 Türkiye


