Credential provider that allows you to use your USB/Bluetooth/NFC security key for passkeys/fido2/u2f authentication.
Cost / License
- Free
- Open Source (Apache-2.0)
Since
- Since 2026
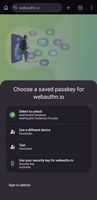

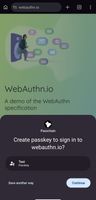


Credential provider that allows you to use your USB/Bluetooth/NFC security key for passkeys/fido2/u2f authentication.

Secure authentication management for your application. Customize as you grow, with easy APIs and programmable workflows. Focus on growing, your login is in good hands.
 Switzerland


OnlyKey is an open source alternative to YubiKey. OnlyKey natively supports: a hardware password manager, multiple two-factor methods (FIDO2, TOTP, and Yubico® OTP), passwordless SSH login, and OpenPGP.
 United States


 Bitwarden Authenticator
Hanko is a modern open source Authentication & User Management system – built and hosted in the EU. Alternative to Clerk, Auth0, Stytch, Descope.
 Germany
 EU

 United States

 2FA Authenticator (2FAS)

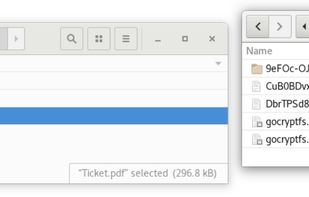
gocryptfs uses file-based encryption that is implemented as a mountable FUSE filesystem. Each file in gocryptfs is stored one corresponding encrypted file on the hard disk. The screenshot below shows a mounted gocryptfs filesystem (left) and the encrypted files (right).
 Cryptomatorand


 Bitwarden Authenticator

Rauthy is a lightweight and easy to use Identity Provider supporting OpenID Connect, OAuth 2.0 and PAM. It aims to be simple to both set up and operate, with very secure defaults and lots of config options, if you need the flexibility.


Stop account takeovers, protect your employees and applications, and eliminate passwords with DIGIPASS® FX7, a FIDO-enabled, phishing-resistant authenticator. DIGIPASS FX7 enhances security while simplifying the login process, enabling a ‘work from anywhere, anytime’ policy.
United States

 2FA Authenticator (2FAS)
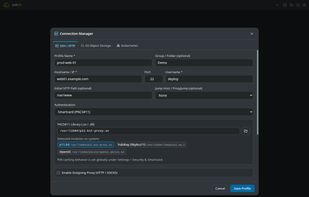
Modern cross-platform SSH, SFTP, S3 & Kubernetes client with smartcard/PKCS#11 auth, split terminal, dual-pane file manager, and sync. Team profile vaults.
 SwedenEU

Plurilock AI Cloud enables users to log in once, at the start of the day, to access all of the applications they use, rather than remembering dozens of usernames and passwords.


RCDevs' OpenOTP Security Suite is an all-in-one enterprise solution for multi-factor authentication (MFA), identity and access management (IAM), single sign-on (SSO), public key infrastructure (PKI), network access control (NAC), and mobile badging.
 LuxembourgEU








 Poland