Cost / License
- Free
- Open Source
Since
- Since 2023


MigrationPilot analyzes PostgreSQL DDL for lock conflicts, missing safeguards, and risky ALTER TABLE patterns. 80 safety rules powered by the real PostgreSQL parser. Features include lock analysis, risk scoring, auto-fix suggestions, safe migration alternatives, and CI/CD...
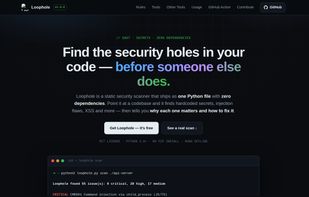
Loophole is a free, open-source (MIT) static security scanner for JavaScript/TypeScript, Python, Go and PHP code, with taint tracking and fix suggestions. It catches hardcoded secrets, SQL injection, XSS, command injection, path traversal, weak crypto and more.


 VirusTotaland

Pyanalyze is a semi-static type checker for Python code. Like a static type checker (e.g., mypy or pyright), it detects type errors in your code so bugs can be found before they reach production. Unlike such tools, however, it imports the modules it type checks, enabling...

Check any threat indicator that you consider suspicious, whether it is a file, file hash, IP address or web address.
 Russia
 VirusTotaland

Open-source i18n QA: a locale-file linter that catches missing keys, dropped placeholders, collapsed plurals and mistranslations in CI — no API key, no account.
 United States

 Crowdinand


Kiuwan Application Security is an end-to-end Appsec platform. Monitoring, action plans and seamless integration within unlocalized teams are but a few of the features offered by Kiuwan.

Improve quality, reduce risk, and ship with confidence. GrammaTech's static analysis SAST tool as part of your secure SDLC identifies bugs that can result in system crashes, unexpected behavior, and security breaches.
United States

nittim scans a GitHub repository for committed secrets and vulnerable dependencies for free, then runs a full security audit that returns findings with evidence and a fix for each. It runs inside Cursor, Claude Code, Windsurf, Codex and Copilot through MCP, or from the web.
codetopo indexes a Rust or Python codebase into a queryable graph of symbols, calls, and imports, and serves it to AI agents over MCP (17 tools), a CLI, and an HTTP API. Free and open source locally (AGPL-3.0) — indexes stay on your machine; a hosted API is US$19/month per key.
 Canada

Scans code, running apps, and cloud config for secrets, dependency risks, misconfigurations, and vulnerabilities, delivering a single grade and actionable plain-English fixes.
 Belgium
 EU


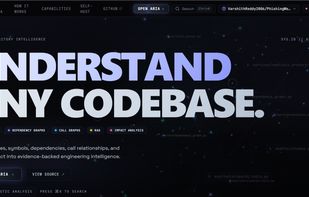
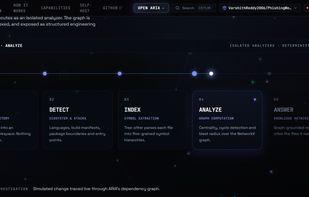
AI-powered repository intelligence platform for understanding unfamiliar codebases through structural code analysis and semantic retrieval.
 India
 opencodeand
 Claude Code

Facebook Infer is a static analysis tool - if you give Infer some Objective-C, Java, or C code, it produces a list of potential bugs.


ProdCanary is a static security review for apps built with AI tools like Lovable, Bolt and Cursor. Upload a zip of your own project and in seconds it flags the mistakes that cause real breaches: hardcoded API keys, Supabase service_role keys in the frontend, missing Row Level...


An artifact of fully-specified annotations to power static-analysis checks, beginning with nullness analysis.


IRIS-H is an online digital forensics tool that performs automated static analysis of files stored in a directory-based or strictly structured formats. The tool produces two types of data views allowing for thorough digital forensics examination.

 VirusTotaland
Free, open-source static scanner that flags FiveM/RedM backdoor patterns: HTTP code loaders, hidden code, obfuscation. Browser version, no upload.

SkillRisk is a specialized security analysis tool designed for the AI Agent ecosystem, specifically focusing on Claude Code and Model Context Protocol (MCP) skills.
 Thailand


 GitHub

RiskAMP is a full-featured Monte Carlo Simulation Engine for Microsoft Excel.
With the RiskAMP Add-in, you can add Risk Analysis to your spreadsheet models quickly, easily, and for a fraction of the price of competing packages.
The PERT distribution for cost and project mod.


Ever received an email with an attachment that felt "off"? Don't risk your computer's security by opening it. Docguard is a dedicated web service designed to help you identify malicious files before they cause harm.
United States VirusTotaland
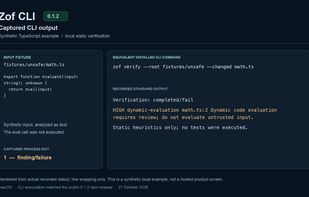
Zof CLI is an open-source command-line tool for inspecting software changes locally. It checks changed source lines for a documented set of static risks and reports findings with severity, file and line information.