Cost / License
- Free
- Open Source
Alerts
- Discontinued
Platforms
- Linux
- Global


One of the most popular alternatives to Wireshark is tcpdump, which is free and open source. Other popular alternatives are NetworkMiner, Proxyman, CloudShark and Ettercap. Network Analyzers like Wireshark are a crowded field, with more than 50 alternatives for Windows, Linux, Mac, Android and the web.

Arcai.com’s NetCut-Defender, –The only one tool can 100% guaranteed success protect you and your user away from arcai.com’s netcut cut (or alike) ARP SPOOFing.
 Taiwan


justniffer is a TCP sniffer. It reassembles and reorders packets and displays the tcp flow in a customizable way. It can log network traffic in web server log format. It can also log network services performances and extract http content.


AirSnare is another tool to add to your Wireless Intrusion Detection Toolbox. AirSnare will alert you to unfriendly MAC addresses on your network and will also alert you to DHCP requests taking place.


Pirni Pro is a network security tool designed for iOS, and specifically for iPhone and iPod Touch devices. It is capable of intercepting traffic on a wireless network segment, capturing passwords, and regular expressions entered by the user.

ByteLens is a free online protocol visualizer and packet analysis tool for TCP, UDP, IPv4, IPv6, DNS, and Ethernet. It helps developers, students, and network engineers parse hex packets, inspect protocol fields, and understand packet structures interactively.

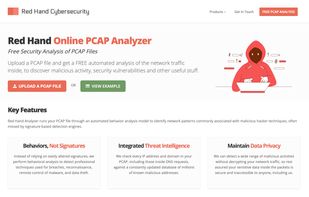
A free, cybersecurity-focused online tool that analyzes PCAP files and generates clear reports highlighting suspicious behaviors, security vulnerabilities, and other notable network events.
 United States

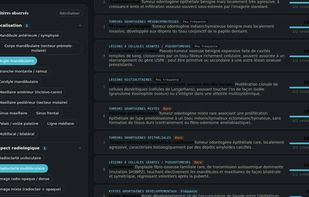
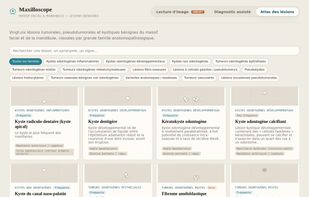
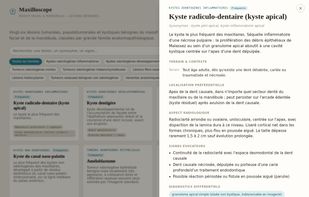
Clinical decision-support tool for oral & maxillofacial radiology. Rank differential diagnoses from imaging criteria, browse an illustrated atlas of 47 lesions, and check red-flag signs of malignancy.
 Cameroon

Free native HTTPS debugging proxy for Mac (Linux beta) with a built-in API client and an MCP server for AI coding assistants.
 India
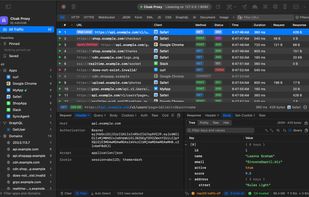
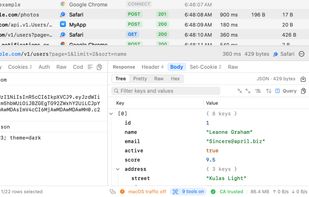
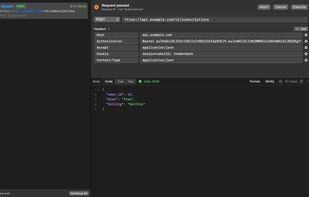
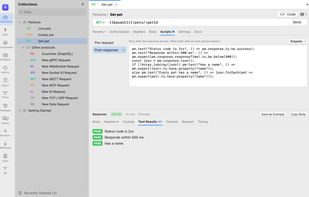

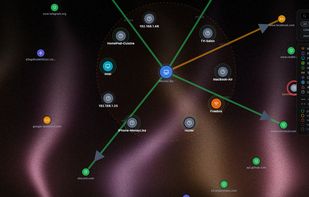
Real-time network traffic visualizer — see every connection your computer makes. Privacy-first, 100% local. / Visualiseur de trafic réseau en temps réel, 100% local.
 France
 EU

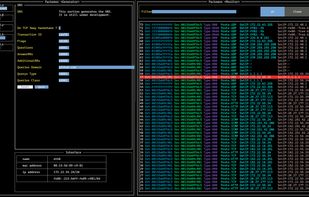
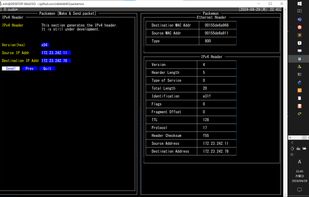
TUI tool for generating packets of arbitrary input and monitoring packets on any network interfaces (default: eth0). The list of interfaces to be specified is output when packemon --interfaces is run. This tool works on Windows, macOS, and Linux.
 Japan
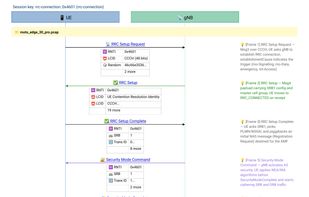
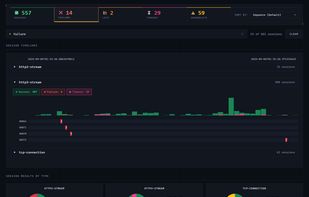
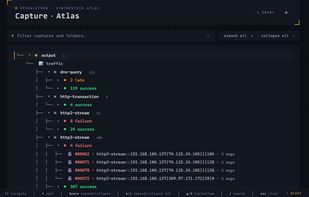
VisualEther turns Wireshark packet captures into readable sequence diagrams — and lets an AI agent reason about them. Built on tshark, it reconstructs multi-layer protocol conversations (5G NR/core, LTE, IMS/VoLTE, SIP/RTP, BGP, OSPF, DNS, HTTP/2 & HTTP/3, TLS, Kerberos...
United States