
SecretDrop.to icon
SecretDrop.to icon

SecretDrop.to

 Like

SecretDrop.to is a free service for sharing one-time secrets. Messages and files are encrypted in your browser before they are uploaded, so the server cannot read what it stores. It deletes a secret after the first retrieval or when it expires.
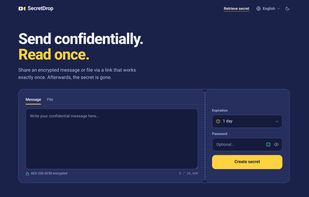
Write a message or add files, choose when it expires and add an optional password.

Cost / License

Since

  • Since 2026

Updated

  • Updated Nov 2026

Platforms

  • Online
  • Tor  [http://secretdimtmcoa7iq2lqkmwmrbze5qknena75f5xlge226jmxfrcg5yd.onion](http://secretdimtmcoa7iq2lqkmwmrbze5qknena75f5xlge226jmxfrcg5yd.onion)
0likes
0articles
Save

Features

Properties

Features

Highlights All activities

SecretDrop.to News & Activities

Recent activities

SecretDrop.to information

AlternativeTo Category

File Sharing

GitHub repository

  •  0 Stars
  •  0 Forks
  •  0 Open Issues
  •   Updated  
View on GitHub
SecretDrop.to was added to AlternativeTo by secretdrop-to on and this page was last updated .

No comments or reviews, maybe you want to be first?

Official Links

What is SecretDrop.to?

SecretDrop.to is a free service for sharing one-time secrets. Messages and files are encrypted in your browser before they are uploaded, so the server cannot read what it stores. It deletes a secret after the first retrieval or when it expires.

You write a message or pick up to 10 files (50 MB in total) and get a link. The recipient opens it once, and then it is deleted. If nobody opens it, it expires after the time you chose: 1 hour to 7 days for messages, up to 3 days for files.

You can add a password, which the recipient needs in addition to the link. The dice button suggests one made of five random words. After five wrong passwords the secret is deleted. Instead of the link you can also send a code or show a QR code.

Before anything is uploaded, your browser removes metadata such as the GPS location from images and gives files random names. There are no accounts, no cookies of our own and no analytics. SecretDrop is also available as a Tor onion service, without Cloudflare and without a third-party bot check.

Encryption uses AES-256-GCM. Without a password, the key stays in the part of the link after the #, which browsers do not send to the server. With a password, the key is derived from it with Argon2id. Everything is padded before encryption, so the stored size reveals little about the content.

The code of the website and the server is open source under AGPL-3.0. A signed warrant canary is renewed at least every 31 days.