Corvus AWPG icon
Corvus AWPG icon

Corvus AWPG

 Like

Corvus AWPG (Active Web Protection Gateway) is a self-hosted gateway that sits in front of your web services. It is as easy to run as Nginx Proxy Manager, with domains, forwarding and free Let's Encrypt certificates set up from a web console in a few clicks, and it also...
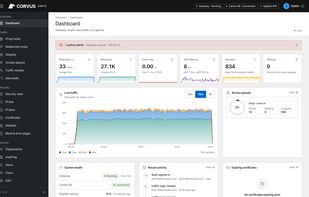
Dashboard: live traffic, access queues and active alerts

Cost / License

Application type

Since

  • New

Updated

  • Updated Nov 2026

Platforms

  • Self-Hosted
  • Docker
0likes
0articles
Save

Features

Properties

Features

Highlights All activities

Corvus AWPG News & Activities

Recent activities

Corvus AWPG information

AlternativeTo Category

Network & Admin

GitHub repository

  •  1 Stars
  •  0 Forks
  •  2 Open Issues
  •   Updated  
View on GitHub
Corvus AWPG was added to AlternativeTo by Jikwang-Moon on and this page was last updated .

No comments or reviews, maybe you want to be first?

Official Links

What is Corvus AWPG?

Corvus AWPG (Active Web Protection Gateway) is a self-hosted gateway that sits in front of your web services. It is as easy to run as Nginx Proxy Manager, with domains, forwarding and free Let's Encrypt certificates set up from a web console in a few clicks, and it also watches, protects and controls the traffic that passes through it. Everything runs on your own server; no traffic is sent to a third-party cloud.

Proxy and TLS

  • Proxy hosts with wildcards, WebSocket, HTTP/2 and forced HTTPS
  • Custom locations (route paths such as /api to another backend), redirection hosts and TCP/UDP streams
  • Let's Encrypt certificates via HTTP-01 or DNS-01 (Cloudflare, DigitalOcean, Hetzner and more) with automatic renewal, or your own certificates
  • Import an existing Nginx Proxy Manager setup: proxy hosts, certificates, streams and access lists

Protection

  • Known attack paths (SQL injection, path traversal, scanner probes) are blocked as soon as a host is added
  • Security rules on IP, country, path, headers or User-Agent lists: block, allow, log or challenge
  • Browser challenge (JavaScript proof of work or cookie check) without third-party CAPTCHA services, and an automatic "under attack" mode
  • Automatic IP bans for repeat attackers with escalating ban times, rate limits, request body inspection and security header presets

Access queue

  • A waiting room for launches and traffic spikes: admit visitors up to your capacity and queue the rest in order

Monitoring and operations

  • Live requests, errors and latency per host and path, searchable request logs with CSV/JSON export
  • Alerts to Slack, Discord, Microsoft Teams, Telegram, Mattermost or webhooks, and Prometheus metrics
  • Every change is tested before it goes live, versioned and can be rolled back
  • Roles, two-step verification, OIDC single sign-on, API tokens, backup and restore

Runs as a single Docker container (amd64 and arm64) built on OpenResty, Go and React. The admin console is available in 8 languages. Licensed under Apache 2.0.