


Burp Suite
49 likes
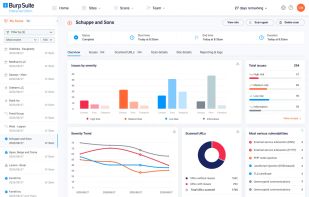
Burp Suite is an integrated platform for performing security testing of web applications. Its various tools work seamlessly together to support the entire testing process, from initial mapping and analysis of an application's attack surface, through to finding and exploiting...

Cost / License
- Freemium (Pay once)
- Proprietary
Application typeApplication types
Platforms
- Mac
- Windows
- Linux
- Flathub
- Flatpak


Features
Highlights All activities
Burp Suite News & Activities
Recent News
No news, maybe you know any news worth sharing?
Share a News Tip
Recent activities
 secman added Burp Suite as alternative to Cloak Proxy
 DonislawDev added Burp Suite as alternative to Naughty Keyboard
- humble-advisor liked Burp Suite
 Maik-Hofmann added Burp Suite as alternative to Quena
 Neon-Web added Burp Suite as alternative to Orb44
- Creative_joe liked Burp Suite
 Conso4s added Burp Suite as alternative to Kayvrn
 incu added Burp Suite as alternative to Vornin
- arberormeni2026 liked Burp Suite
- Krishna-Kumar added Burp Suite as alternative to Xalgorix


Developed by
 PortSwigger Ltd.
Licensing
Proprietary and Freemium product.Pricing
One time purchase (perpetual license) + free version with limited functionality.Alternatives
47 alternatives listedBadge
Get an embeddable badge for Burp SuiteSupported Languages


Best Tools of Penetration Test for Noobies
A list with 10 apps by ulyanov92 without a description.


Cyber security list
A list with 21 apps by MartinO without a description.


Reverse Engineering and tinkering
A list with 11 apps by bads_tm without a description.
Comments and Reviews
The subject of the thread summarises what I experienced when working with this software. An unfriendly UI, which is hard to interact with, is messing up my first steps into using this product