Post-quantum file encryption built on the age protocol. Seal a file to a quantum-safe ML-KEM-768 hybrid key, sign it with a YubiKey over NFC, and hand it to anyone with the age CLI. Any size you like: a 1 GB file encrypts like a small one.
The file you send today gets read twice.
Once by the person you sent it to. Possibly again, years later, by whoever kept a copy.
Encrypted traffic gets recorded and stored. It does not need to be readable at the time. The bet is that a cryptographically relevant quantum computer eventually arrives, and every X25519 file in the archive opens at once. The industry calls it harvest now, decrypt later, and it is the reason a file with a long secrecy lifetime needs more than good classical crypto today.
A signature that keeps your name out of it.
Sign then encrypt, so the ciphertext gives nothing away.
A detached signature sitting next to a file is readable. Anyone who intercepts the pair can lift the signer's public key straight off it and learn who sent the file without decrypting anything. From 3.0 AgePony signs the plaintext, packs the payload and its signature together, and encrypts the whole thing. One file goes out. The recipient learns who signed it only once they can already read it.
01 - Pick files
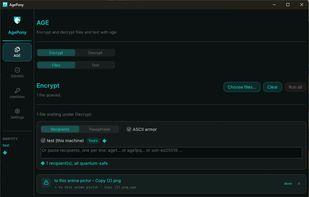
One file or many, of any size. Several can become one archive or one encrypted file each.
02 - Choose a recipient
A GitHub username, an SSH key, a classical age recipient, a post-quantum one, or just a passphrase.
03 - Sign it (optional)
Flip one switch and the signature is sealed inside the file, made with a key, the Secure Enclave, or a tap of your YubiKey.
04 - Seal it
AgePony writes a real age file. Share it however you like, it is just bytes.






 NorseHorse


