


Automatically reviews code style, security, duplication, complexity, and coverage on every change while tracking code quality throughout your sprints.
Cost / License
- Free Personal
- Open Source
Since
- Since 2014
 Portugal
 EU


+4


Apps similar to SonarQube include Codacy, which is open source and free for personal use. Other options are Shellcheck, Cppcheck, Coverity Scan and VibeGuard. You're spoiled for choice with Code Reviews like SonarQube: we list more than 25 alternatives for the web, Windows, Linux, Mac and self-hosting.
Automatically reviews code style, security, duplication, complexity, and coverage on every change while tracking code quality throughout your sprints.
PortugalEU
 Norway


Cppcheck is an static analysis tool for C/C++ code. Unlike C/C++ compilers and many other analysis tools it does not detect syntax errors in the code. Cppcheck primarily detects the types of bugs that the compilers normally do not detect.
 SwedenEU


Coverity Scan Static Analysis allows to find and fix defects in your Java, C/C++ or C# open source project for free.

CodeTruss makes every agent change prove it belongs. Its local Boundary records the task and starting Git state, checks scope and sensitive surfaces, runs 13 deterministic registry analyzers plus project verification, and writes an integrity-signed receipt.


SlowQL is a production-focused offline SQL static analyzer that catches security vulnerabilities, performance regressions, reliability issues, compliance risks, cost inefficiencies, and code quality problems before they reach production.
 Canada


Semgrep is a fast, open-source, static analysis tool that excels at expressing code standards — without complicated queries — and surfacing bugs early at editor, commit, and CI time. Precise rules look like the code you’re searching; no more traversing abstract syntax trees or...

Flawfinder examines C/C++ source code and reports possible security weaknesses ("flaws'') sorted by risk level. It's very useful for quickly finding and removing at least some potential security problems before a program is widely released to the public.
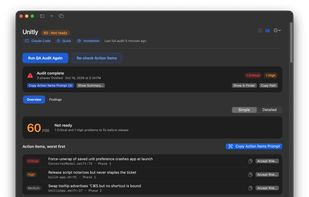
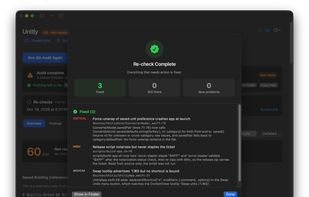
Native macOS app that runs release-readiness QA audits on Mac app projects and tracks findings across audits and re-checks.
 United States


SAST Online has come a long way from its beginnings for Global. SAST online targeted to analyse your code without installing or opening terminal.


 Netherlands


