


AI-powered GitHub repository health analysis — get instant health scores, risk signals, and contributor insights for any repo from a single URL.
Cost / License
- Freemium
- Proprietary
Platforms
- Software as a Service (SaaS)
- Online
 United Kingdom


Apps similar to SonarQube include Codacy, which is open source and free for personal use. Other options are Shellcheck, Cppcheck, Coverity Scan and VibeGuard. You're spoiled for choice with Code Reviews like SonarQube: we list more than 25 alternatives for the web, Windows, Linux, Mac and self-hosting.
AI-powered GitHub repository health analysis — get instant health scores, risk signals, and contributor insights for any repo from a single URL.
United Kingdom
Code Inspector is a platform that helps developers and managers to deliver better code. Main features:


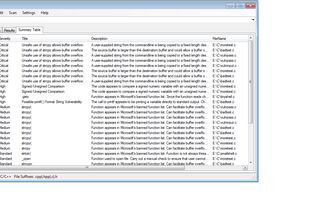
VCG is an automated code security review tool that handles C/C++, Java, C#, VB and PL/SQL. It has a few features that should hopefully make it useful to anyone conducting code security reviews, particularly where time is at a premium:

Get high-quality feedback on every Pull Request. Only pay for developers who actively ship code — unlimited reviews, no per-seat waste.
 Netherlands
 EU


Exlint is a an open source project that enables developers to centralize their open source coding standards and policies, so that configuring repositories becomes as easy as typing one command.
 Israel


Parasoft’s C/C++test is the fully-integrated software testing solution for embedded safety-critical industries. Its automated software testing capabilities are also made for today’s high-velocity Agile DevOps environments.


Appfora helps software teams finish the essential work around a product that is often postponed until launch. It analyses a repository or product source and builds four code-grounded pillars. Legal drafts Terms, Privacy, Acceptable Use, Payment, Disclosure and Communications...
United Kingdom
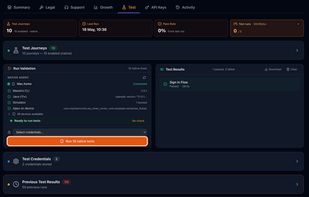


AI-powered code review and release management: security and compliance scanning, documentation generation, and observability instrumentation, from PR to production.


Improve quality, reduce risk, and ship with confidence. GrammaTech's static analysis SAST tool as part of your secure SDLC identifies bugs that can result in system crashes, unexpected behavior, and security breaches.
 United States


DefenseCode ThunderScan® is a SAST (Static Application Security Testing, WhiteBox Testing) solution for performing deep and extensive security analysis of application source code.
United Kingdom


Qodana is a smart code quality platform by JetBrains best suited for working in teams. It can analyze code written in 60+ languages including Java, JavaScript, TypeScript, PHP, Kotlin, Python, Go, and C#.


Examines codebases for secrets, dependency risks, and unsafe API keys, checks running apps for TLS and security headers, and analyzes Supabase, Firebase, and Firestore configs for exposure—then provides a single grade, report, and actionable fixes.
 BelgiumEU


 Czechia


