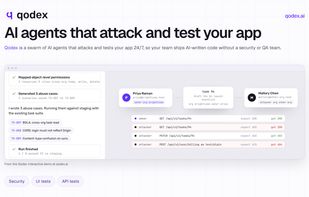
Qodex is a swarm of AI agents that attacks and tests your app 24/7, so your team ships AI-written code without a security or QA team.
The problem: your team ships with coding agents, so the code doubles and the people who test and secure it do not. 45% of AI-written code fails OWASP Top 10 security tests (Veracode, 2025). Your pentest is once a year.
What Qodex does: a swarm of agents runs against your live app. The largest group tries to break in the way a hacker would: injection, broken auth, one customer seeing another customer's data, the OWASP Top 10 and the OWASP API Top 10, with the exploit reproduced as evidence. The others click through every screen in a real browser and call every API, from an OpenAPI, Swagger or Postman import.
How you drive it: describe what to attack or test in plain English and watch it work live. It remembers your app across sessions: auth, quirks, past bugs, your code if you link the repo.
What you keep: every test is saved as plain Playwright or HTTP code you own. Saved tests re-run with no AI calls, every night, from CI on every deploy, or from Claude Code and Cursor. When a screen changes, a saved step finds its control again from the intent.
What you get back: every failure labelled real bug, stale test or environment problem, with severity, steps and evidence. A security test passes only when the attack was blocked.
Start: free plan, no card. Paid from $1,299 per project per month. Managed cloud, AWS Marketplace or self-host.









No comments or reviews, maybe you want to be first?