Cost / License
- Free
- Proprietary
Platforms
- Windows
 Sweden
 EU


Apps similar to Packet Capture include Wireshark, which is free and open source. Other options are mitmproxy, InterceptSuite , tcpdump and NetworkMiner. There's no shortage of Network Analyzers like Packet Capture, with more than 25 alternatives for Windows, Linux, Mac, Android and self-hosting.
SwedenEU
Mojo Packets™ is web based tool that simplifies trace based analysis and troubleshooting of connectivity/performance issues observed in Wi-Fi (IEEE 802.11) environments.
 United States


Packetsdump is a free sniffer tool, it is also a general purpose network diagnostic tool for LAN administrators, security professionals, programmers and students who are interested in network traffic transmitted between PC and the whole LAN.
 China


PlayCap plays back captures made from Wireshark, tcpdump, WinDump, or any libpcap-based application. PlayCap was originally (and still is) a part of IG Scanner by Signal 11 Software, but was spun off as a separate app and released as Open Source software.


Timesketch is an open-source tool for collaborative forensic timeline analysis. Using sketches you and your collaborators can easily organize your timelines and analyze them all at the same time. Add meaning to your raw data with rich annotations, comments, tags and stars.
United States


If you're debugging on a remote machine with a large pcap and no desire to scp it back to your desktop, termshark can help!

httpry is a tool designed for displaying and logging HTTP traffic. It is not intended to perform analysis itself, but instead to capture, parse and/or log the traffic for later analysis. It can be run in real-time displaying the live traffic on the wire, or as a daemon process...
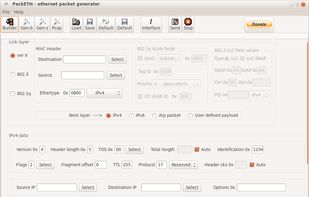
packeth is GUI and CLI packet generator tool for ethernet. Primary it is developed and maintained for Linux, but some ports for Windows and MAC have also be done. It allows you to create and send any possible packet or sequence of packets on the ethernet link.
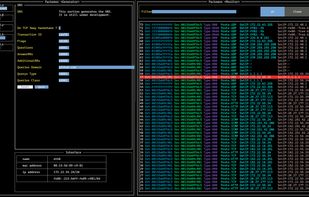
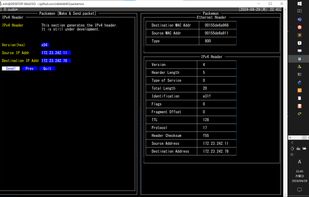
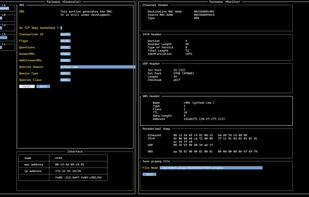
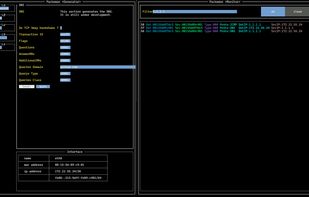
TUI tool for generating packets of arbitrary input and monitoring packets on any network interfaces (default: eth0). The list of interfaces to be specified is output when packemon --interfaces is run. This tool works on Windows, macOS, and Linux.
 Japan

justniffer is a TCP sniffer. It reassembles and reorders packets and displays the tcp flow in a customizable way. It can log network traffic in web server log format. It can also log network services performances and extract http content.


HttpCanary is a powerful HTTP/HTTPS/HTTP2/WebSocket/TCP/UDP packets capture and analyzer app designed for Android platform.