




OpenShell
Like
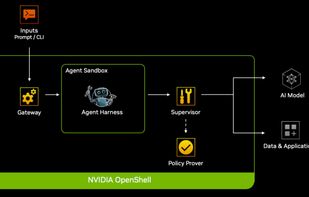
NVIDIA OpenShell is an open, secure runtime for agents. It governs agent execution, access, and where inference goes.

Cost / License
- Free
- Open Source (Apache-2.0)
Platforms
- Rust
- Linux
- Mac
- Windows

Features
OpenShell News & Activities
Highlights All activities
Recent News
- Paul published news article about OpenShell

Recent activities

OpenShell information
Developed by
 NVIDIA
Licensing
Open Source (Apache-2.0) and Free product.Written in
Alternatives
4 alternatives listedBadge
Get an embeddable badge for OpenShellSupported Languages

AlternativeTo Categories
Development, Security & Privacy, System & HardwareGitHub repository
- 10,355 Stars
- 1,402 Forks
- 481 Open Issues
- Updated


No comments or reviews, maybe you want to be first?