

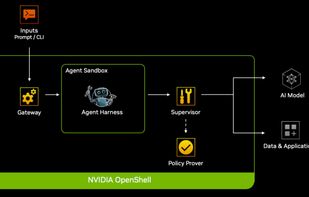
NVIDIA OpenShell is an open, secure runtime for agents. It governs agent execution, access, and where inference goes.
Cost / License
- Free
- Open Source (Apache-2.0)
Since
- New
 United States

Best alternatives are 

5 alternatives


NVIDIA OpenShell is an open, secure runtime for agents. It governs agent execution, access, and where inference goes.
United States
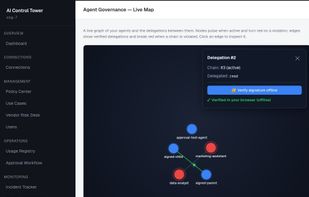
AI Control Tower is an open-source, self-hosted platform for governing, auditing, and overseeing enterprise AI usage. It runs entirely inside an organization's own network — no external SaaS dependency, no data leaving the perimeter.

ZeusLock DLP prevents sensitive data leaks to AI by detecting, anonymizing or blocking API keys, passwords, card numbers, IBANs and personal data in real time.

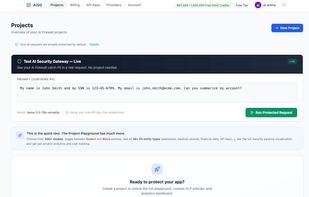
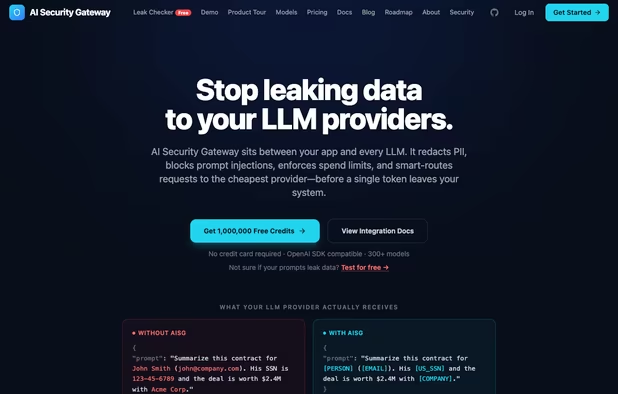
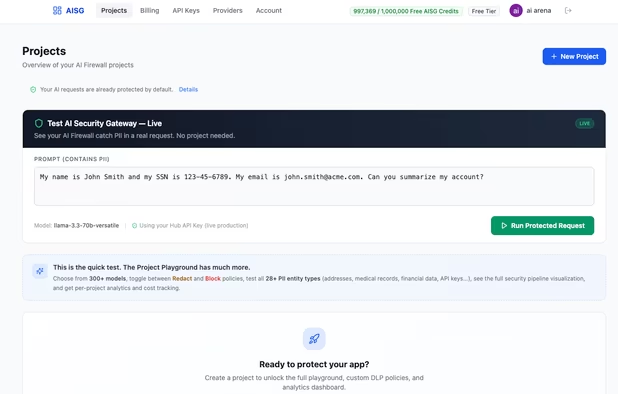
Open-source AI firewall and LLM proxy that redacts PII, blocks prompt injection, and enforces spend budgets before requests reach any AI provider. Cloud SaaS, Hybrid VPC and Apache 2.0, self-hostable.
United States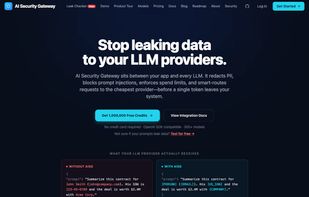

 Experiential
AgentSecrets is open-source, zero-knowledge credential infrastructure designed for the AI era.
 Nigeria

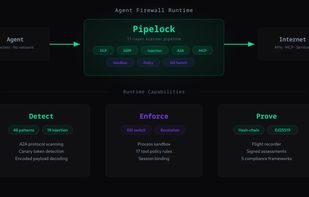
Pipelock is an open-source agent firewall written in Go. It runs as a sidecar or local service between an agent and the network, scanning HTTP, WebSocket, and Model Context Protocol traffic through an 11-layer pipeline.
United States


AI that blocks hackers while you sleep. Runs on cheap hardware. When someone in Tokyo gets attacked, you're protected in 30 seconds. No fees. No experts needed. Just protection.
 Romania
 EU

AgentGuard is an SDK for AI agent developers that enforces budget limits, auth isolation, and MCP policy rules. Stop agents from overspending, leaking data, or exceeding their permissions. Works with any LLM stack.

AI-driven black-box testing identifies and validates novel vulnerabilities, logic flaws, and attack paths with custom remediation and automated retesting.
 Israel


iDox.ai Guardrail is an AI security platform designed to prevent sensitive data leaks across AI tools, copilots, and autonomous agents. It monitors, intercepts, and sanitizes prompts, file uploads, and AI-generated responses in real time—before data leaves the user’s device.
United States


 Microsoft Defender

Alice (formerly ActiveFence) is an enterprise AI security platform built on nearly a decade of adversarial intelligence. WonderSuite brings together three tools for the full AI lifecycle: WonderBuild for pre-launch red teaming and stress testing, WonderFence for real-time LLM...


Discover and compare open-source Agent Skills, tools & MCP servers — with quality scoring, trending analysis, and automated GitHub sync.


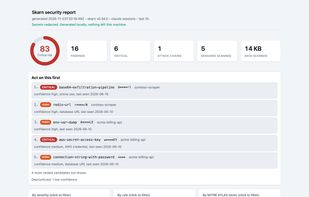
AI coding session security scanner: finds leaked credentials and prompt-injection-to-exfiltration attack chains in the session logs AI coding assistants write to disk, entirely on the machine.
 EstoniaEU


HOL Guard is an open-source, local-first runtime security layer for AI agents and automation. It sits between any AI harness and the tools it wants to run, pausing risky package installs, secret reads, shell commands, and MCP changes for review before execution.
 Marshall Islands


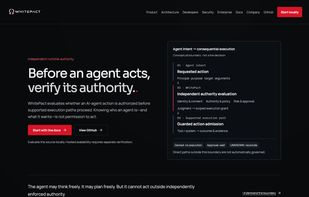
WhitePact is an open-source runtime authority and governance layer for AI agents and autonomous systems. It sits between agent intent and consequential execution, evaluating identity, authority, intent, policy, risk and approval before an action is allowed to proceed.
 India

AI agent governance middleware providing PII detection, policy enforcement, compliance receipts, and kill switch for AI agents.
 Australia


 GitHuband

Self-hosted gateway that inspects browser, API and coding-tool AI traffic, masks sensitive data, blocks requests, and enforces model access policies.
 Türkiye
 Experientialand


AlertKick is an affordable on-call alerting and incident notification platform built for DevOps engineers at startups and SMBs - a great no-configuration monitoring and security without the enterprise pricing.
 United Kingdom


 Uptime Kumaand

Cirvix decides every tool call your AI agent makes before it runs: permit, hold for approval, or deny. Local and default-deny, with an MCP gateway, adapters, and a SHA-256 audit chain.


Tragentics is the AI agent security platform that authenticates every agent, injects keys from an encrypted Credential Vault so agents never hold them, routes every call through a content-blind relay, and records a metadata-only audit trail — across platforms and protocols.
United States


Sentinel.AI helps protect against prompt injection attacks, credential leaks, and risky prompts in AI chat interfaces like ChatGPT, Claude, and similar platforms. The extension runs entirely locally on your machine - no data is sent to external servers.
 Canada


Open-source desktop security for local AI agents, with skill/configuration reviews, alerts, selected-process controls and policies on configured command-line and MCP routes. Windows-first beta.


Enoki is an AI red teaming platform that tests AI agents for security, safety and policy risks. It attacks the deployed agent through its endpoint the way an adversary would, over multiple turns, shows the exact attack and the agent's response behind every finding, and...
 BelgiumEU


AI Agent Security Testing — 112 attacks across 14 categories. Prompt injection, jailbreaks, MCP poisoning, agency hijacking & more. Test any AI agent in 5 minutes.


 France








 Germany