


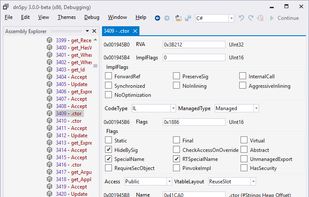
dnSpy is a debugger and .NET assembly editor. You can use it to edit and debug assemblies even if you don't have any source code available.
Platforms
- Windows



+3
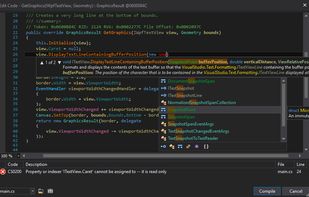


dnSpy is a debugger and .NET assembly editor. You can use it to edit and debug assemblies even if you don't have any source code available.

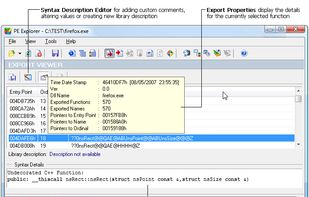
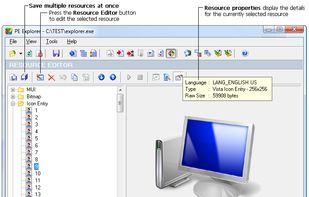
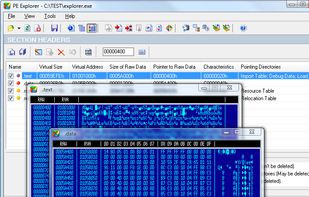
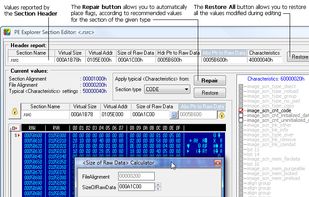
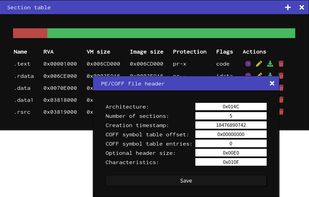
PE Explorer is the most feature-packed program for inspecting the inner workings of your own software, and more importantly, third party Windows applications and libraries for which you do not have source code.
 Canada


One MCP for reverse engineering across binaries, applications, and runtime behavior.
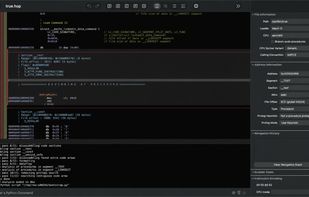


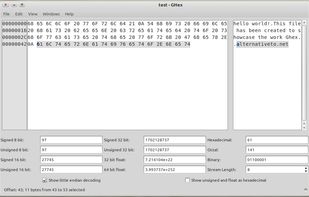
GHex - a hex editor for GNOME
GHex allows the user to load data from any file, view and edit it in either hex or ascii.
Useful for debugging problems with object code or encodings.
Also used by kids who cheat at computer games, by adding score or lives to saved games.


angr is an open-source binary analysis platform for Python. It combines both static and dynamic symbolic ("concolic") analysis, providing tools to solve a variety of tasks.


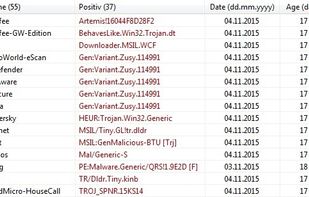
pestudio implements a rich set of features that is especially designed to retrieve every single detail of any executable file. Results are checked against the Microsoft specification. Additionally, the content of the file being analyzed is checked against several white and black...


BinEd is a hex editor tool, which allows to directly browse and edit content of any file or binary data.
 Czechia
 EU
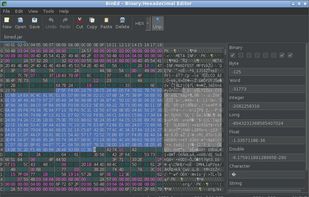
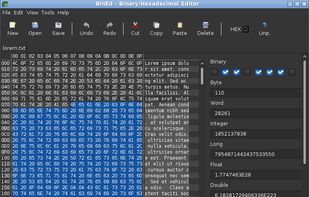
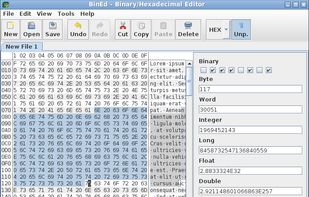
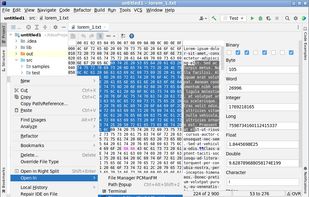


A cross-platform (Windows, Linux, Mac, BSD) hex editor for reverse engineering, and everything else.
 United Kingdom




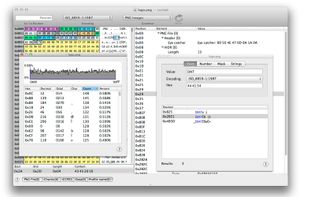
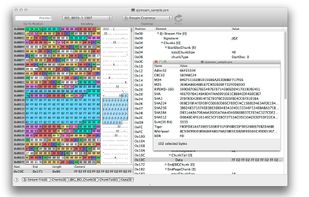
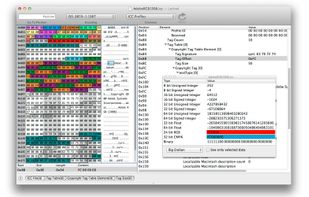
You got a binary file and don't know its contents. Or some software creates binary files where you have a specification but don't want to decode them manually.
 GermanyEU



Hiew (short for Hackers view) is a popular console hex editor for DOS and Windows written by Eugene Suslikov (sen). Amongst its feature set is its ability to view files in text, hex and disassembly mode.
 Russia


 Italy


 United States


