




depproof
Like
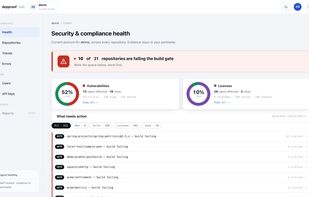
Self-hosted dependency security scanner that finds vulnerable third-party dependencies across your full tree, ranks them by active exploitation, and generates a CycloneDX SBOM.

Cost / License
- Freemium (Usage-based)
- Proprietary
Platforms
- Self-Hosted
- Linux
- Docker


Features

depproof News & Activities
Highlights All activities
Recent activities
- Prasad Vara added depproof
 Prasad Vara added depproof as alternative to Snyk, Patchdex, Mend Renovate, Aikido Security and 13 more

depproof information
Developed by
depproofLicensing
Proprietary and Freemium product.Pricing
Usage-based pricing (pay per credit or per use) + free version with limited functionality.Alternatives
17 alternatives listedBadge
Get an embeddable badge for depproofSupported Languages


No comments or reviews, maybe you want to be first?