Apps tagged with 'Sbom'

All apps in Apps tagged with 'Sbom' category. Use the filters below to narrow down your search. 
Copy a direct link to this comment to your clipboard
  1. Software supply chain attacks are on the rise and with it, the need to build transparent, evidence-based trust in software.

    Cost / License

    • Subscription
    • Proprietary

    Since

    • Since 2023

    Platforms

    • Mac
    • Linux
    • Online
    • Software as a Service (SaaS)
    • Google Chrome
    Scribe Security screenshot 1
    2 alternatives
  2. ReARM icon
     1 like

    ReARM is an abbreviation for "Reliza's Artifact and Release Management". It is a Release Governance Platform to manage lifecycle for product and component releases and organize release metadata, including SBOMs, xBOMs, other security artifacts, vulnerability...

    Cost / License

    • Freemium (Subscription)
    • Open Source (AGPL-3.0)

    Since

    • Since 2026

    Platforms

    • Online
    • Software as a Service (SaaS)
    • Self-Hosted
    • Docker
    • CA flagCanada
    Changes in SBOM components detected by ReARM
    Findings showing for a release in ReARM
  3. Mend.io icon
     7 likes

    Mend.io offers the first AI native application security platform, purpose-built to secure AI-generated code and embedded AI components. Our unified platform enables companies to manage application risk effectively in modern software development.

    Cost / License

    • Subscription
    • Proprietary

    Since

    • Since 2014

    Platforms

    • Online
    • Software as a Service (SaaS)
    • Self-Hosted
    • IL flagIsrael
    Mend.io screenshot 1
    Mend.io screenshot 1
    Mend.io screenshot 2
    33 alternatives
  4. HodeiShield icon
     1 like

    Security, compliance and third-party risk platform for regulated organisations worldwide: signed endpoint evidence, FAIR risk in euros, multiple frameworks and attestations anyone can verify offline.

    Cost / License

    • Subscription
    • Proprietary

    Since

    • New

    Platforms

    • Windows
    • Mac
    • Linux
    • Online
    • ES flagSpain
    • European Union flagEU
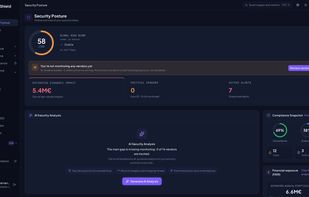
    Security Posture (dashboard)
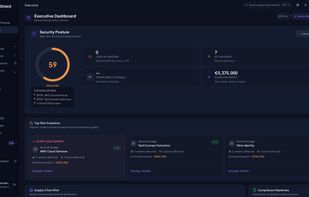
    Executive Dashboard
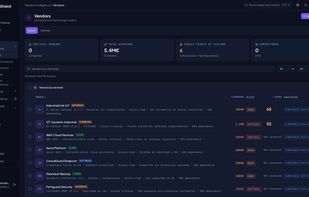
    Vendors (TPRM list, exposure, score)
    +5
    Compliance overview (posture, 17-framework radar)
    19 alternatives
  5. Vornin icon
     Like

    European vulnerability management. Scan your attack surface, resolve findings, and prove compliance with audit-grade evidence.
    Cost / License

    • Freemium (Subscription)
    • Proprietary

    Application type

    Since

    • New

    Platforms

    • Online
    • Software as a Service (SaaS)
    Risk-prioritised findings with CVSS, EPSS and CISA KEV exploit signals.
    Finding detail with AI triage, remediation steps and false positive scoring.
    Every finding auto-mapped to the controls it touches across 9 frameworks, including NIS2, DORA, SOC 2 and ISO 27001.
    +2
    Security controls continuously tested; export a tamper-evident auditor pack.
    14 alternatives
  6. Vibgrate icon
     Like

    Local CLI that scores dependency and runtime drift, checks known vulnerabilities, maps code relationships, and ranks upgrade work for CI.

    Cost / License

    Application type

    Since

    • New

    Platforms

    • Windows
    • Mac
    • Linux
    • Online
    • Software as a Service (SaaS)
    • Docker
    • GB flagUnited Kingdom
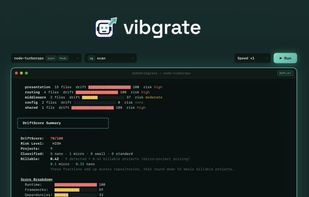
    Vibgrate screenshot 1
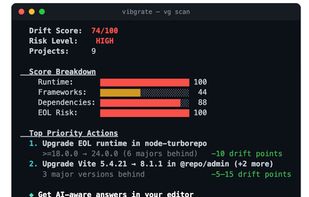
    One command scans any repo for upgrade drift — a 0–100 DriftScore, the vulnerabilities hiding in stale dependencies, and the upgrade path to clear them.
    DriftScore in VS Code - The number, what’s in it, the EOL horizon, and a 90-day trend — one click from the activity bar.
    +2
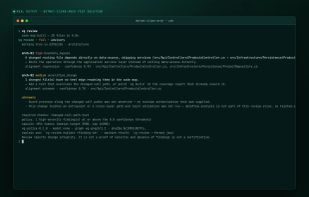
    A vg review scan showing a breach of the declared architecture boundary by a Controller reaching the persistence layer.
    14 alternatives
  7. European artifact repository SaaS for secure software supply chains, with package repositories, SBOMs, vulnerability visibility, access control, and CRA-relevant workflows.

    Cost / License

    • Subscription
    • Proprietary

    Application type

    Since

    • Since 2026

    Platforms

    • Online
    • Software as a Service (SaaS)
    • DE flagGermany
    • European Union flagEU
    Explore container repositories with namespaces, tags, digests, and metadata. Craftifact shows platform information, image size, and upload history for full transparency.
    Browse artifacts stored in a repository and inspect detailed metadata such as uploader, timestamps, download history, and repository path.
    Generate scoped API tokens for Maven, Python, npm, go, and OCI registries. Tokens can have configurable expiration times and are ideal for CI/CD pipelines, build systems, and automated deployments.
    +9
    Create robot accounts with dedicated access tokens for CI/CD workflows, automated builds, and deployments with configurable permissions and token rotation.
    8 alternatives
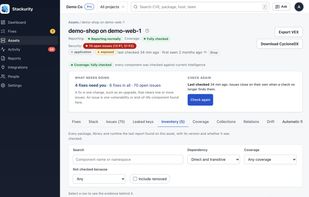
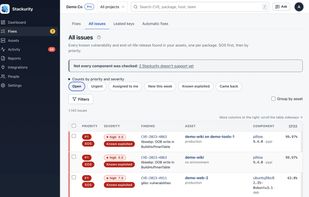
  8. Continuously know what's running, what's vulnerable, what's exposed and what needs fixing. Then verify every fix.
    Cost / License

    Application type

    Since

    • New

    Platforms

    • Online
    • Software as a Service (SaaS)
    • Self-Hosted
    • Docker
    • Kubernetes
    Inventory: every package, library and runtime found on an application
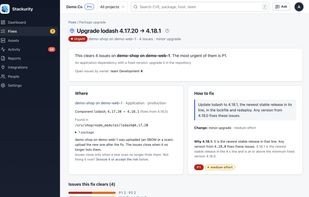
    Prioritised findings: P1 to P4, known-exploited issues first
    A fix: one upgrade that clears several issues, with the version to move to
    +1
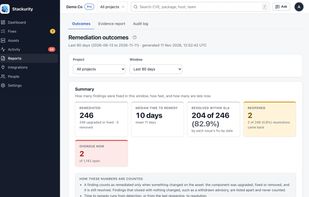
    Fix verification: remediation outcomes counted only when a new check confirms the change
    13 alternatives
  9. depproof icon
     Like

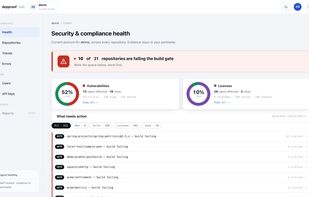
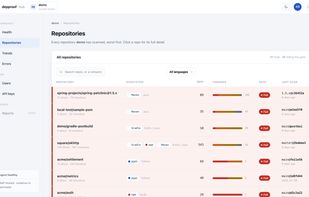
    Self-hosted dependency security scanner that finds vulnerable third-party dependencies across your full tree, ranks them by active exploitation, and generates a CycloneDX SBOM.
    Cost / License

    • Freemium (Usage-based)
    • Proprietary

    Application type

    Since

    • New

    Platforms

    • Linux
    • Self-Hosted
    • Docker
    depproof screenshot 1
    depproof screenshot 1
    depproof screenshot 2
    +1
    depproof screenshot 3
    17 alternatives
  10. sbomify icon
     Like

    sbomify is the trust center for your software supply chain. Store every SBOM and compliance document in one place, track them across products and releases, and share them with customers and regulators on demand. CycloneDX and SPDX, built for EU CRA compliance.

    Cost / License

    Since

    • Since 2026

    Platforms

    • Linux
    • Online
    • Docker
    • GB flagUnited Kingdom
    sbomify screenshot 1
    sbomify screenshot 1
    sbomify screenshot 2
    +13
    sbomify screenshot 3
    6 alternatives
  11. Generates SBOMs during CI from lockfiles, containers, and directories using native tooling with ecosystem coverage, metadata enrichment, trusted outputs, and OIDC publishing.

    Cost / License

    Since

    • Since 2026

    Platforms

    • Linux
    • Docker
    • GB flagUnited Kingdom
    sbomify action screenshot 1
    1 alternative
  12. SCANOSS icon
     Like

    SCANOSS is the first affordable, open OSS Inventory & Intelligence platform that was built specifically for modern DevSecOps and supply chains. Empowering them to deliver greater license, security, quality and provenance visibility and control for DevSecOps teams and their...

    Cost / License

    • Freemium (Subscription)
    • Open Source (MIT)

    Since

    • Since 2024

    Platforms

    • Windows
    • Mac
    • Linux
    • Self-Hosted
    • Python
    • GB flagUnited Kingdom
    SCANOSS screenshot 1
    SCANOSS screenshot 1
    2 alternatives