WaxSeal is for organisations that have to give a specific person a secret — an API key, a temporary credential, bank details, a recovery code — and keep authority over it afterwards.
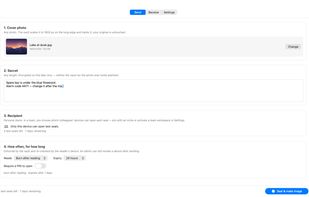
The sender encrypts the text on their own device, for the recipients' devices. The ciphertext is held in a vault the organisation controls and which cannot read it, and the photo that travels carries only a small sealed reference rather than the data. That photo then goes over WhatsApp, WeChat, email or anything else, and the invisible reference survives the compression and resizing those platforms apply to images. On its own the photo reveals nothing and opens nothing.
The recipient opens it in WaxSeal, authorised on their own device with Face ID or Touch ID. The sender sets the rules and can still change them after sending: open once, expire on a date, limit the number of reads, require a PIN delivered by another channel, or revoke. Revoking prevents any further authorised opening — it cannot un-show something a person has already read, so a credential you no longer trust still gets rotated.
Because nothing travels as a secret-bearing URL, there is no link for a chat preview bot or a mail scanner to fetch and spend before the recipient gets there.
The apps are a free download for iPhone, iPad and Mac and include three self-addressed test seals, with no account required. Recipients never pay. Sending to other people needs a team workspace, priced per organisation; a self-hosted edition keeps the vault on your own servers. WaxSeal carries text, not files.






 harrisonsec added WaxSeal as alternative to One-Time Secret, Privnote, Yopass, Password Pusher and 10 more


No comments or reviews, maybe you want to be first?