




Stackurity
Like
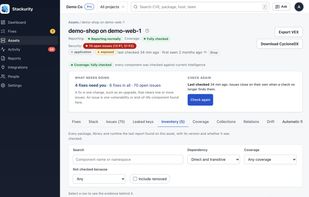
Continuously know what's running, what's vulnerable, what's exposed and what needs fixing. Then verify every fix.

Cost / License
- Freemium (Subscription)
- Open Source (Apache-2.0)
Application type
Since
- New
Updated
- Updated Nov 2026


Features
Highlights All activities
Stackurity News & Activities
Recent activities
 Mauricio B. Holguin added Stackurity as alternative to ArtefactFlow
- Stackurity added Stackurity
- Paul updated Stackurity
- Stackurity updated Stackurity
 Stackurity added Stackurity as alternative to Snyk, Dependabot, Wiz, Nessus and 9 more


Developed by
StackruityLicensing
Open Source (Apache-2.0) and Freemium product.Pricing
Subscription that costs up to $79 per month + free version with limited functionality.Written in
Alternatives
14 alternatives listedBadge
Get an embeddable badge for StackuritySupported Languages
AlternativeTo Category
Security & PrivacyGitHub repository
- 6 Stars
- 0 Forks
- 35 Open Issues
- Updated


No comments or reviews, maybe you want to be first?