


Automatically reviews code style, security, duplication, complexity, and coverage on every change while tracking code quality throughout your sprints.
Cost / License
- Free Personal
- Open Source
Since
- Since 2014
 Portugal
 EU


+5


The best open source alternative to SonarQube is Codacy. It's not free, so if you're looking for a free alternative, you could try Codacy or Shellcheck. If that doesn't suit you, our users have ranked more than 25 alternatives to SonarQube and 16 is open source so hopefully you can find a suitable replacement. Other interesting open source alternatives to SonarQube are Repowise, VibeGuard, SlowQL and Semgrep.
Automatically reviews code style, security, duplication, complexity, and coverage on every change while tracking code quality throughout your sprints.
PortugalEU
 Norway


Cppcheck is an static analysis tool for C/C++ code. Unlike C/C++ compilers and many other analysis tools it does not detect syntax errors in the code. Cppcheck primarily detects the types of bugs that the compilers normally do not detect.
 SwedenEU


SlowQL is a production-focused offline SQL static analyzer that catches security vulnerabilities, performance regressions, reliability issues, compliance risks, cost inefficiencies, and code quality problems before they reach production.
 Canada


Semgrep is a fast, open-source, static analysis tool that excels at expressing code standards — without complicated queries — and surfacing bugs early at editor, commit, and CI time. Precise rules look like the code you’re searching; no more traversing abstract syntax trees or...

Flawfinder examines C/C++ source code and reports possible security weaknesses ("flaws'') sorted by risk level. It's very useful for quickly finding and removing at least some potential security problems before a program is widely released to the public.

PhpMetrics provides metrics about PHP project and classes, with beautiful and readable HTML report.


High-precision Python SAST & Dead Code Remover. Finds unused functions, secrets, and security flaws with hybrid static analysis + local LLM agents. Privacy-first & low noise. MCP server for SAST too.
 Singapore


Code Buster reports dependency wiring, dead code, cycles, duplication, complexity, architecture-policy violations, feature flags, security and style heuristics, quality scores, and remediation plans.
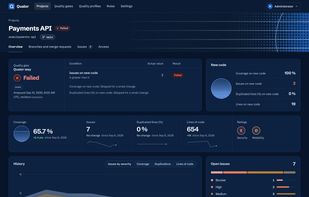
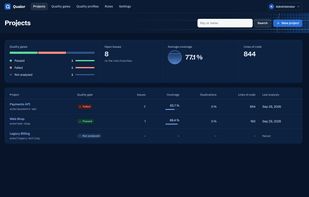
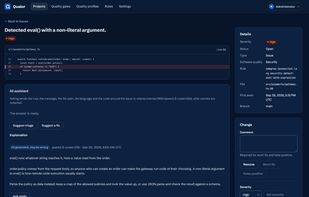
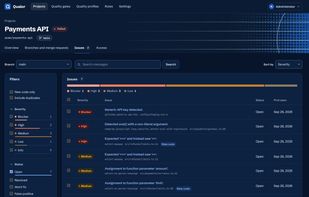
Open-source, self-hosted code quality platform: a SonarQube alternative without lines-of-code licensing. Qualor runs existing open-source analyzers, tracks their issues across commits, measures coverage, duplication and complexity, and applies a quality gate to new code.
 FinlandEU


 Netherlands


 United States


