


PackageFix is a free browser-based dependency security fixer. Paste your manifest file and get back a fixed version with every vulnerable package patched — ready to download in one click.
Platforms
- Online
 United States


Sites and apps similar to Snyk include GitHub, which has a free version. Other options are Patchdex, Artemis Security Scanner, Mend Renovate and Metaport. You're spoiled for choice with Vulnerability Scanners like Snyk: we list more than 25 alternatives for Mac, Windows, Linux, self-hosting and Android.
PackageFix is a free browser-based dependency security fixer. Paste your manifest file and get back a fixed version with every vulnerable package patched — ready to download in one click.
United States
Security API for AI agents to detect prompt injection, jailbreak attempts, and unsafe operational intent before execution.


Examines codebases for secrets, dependency risks, and unsafe API keys, checks running apps for TLS and security headers, and analyzes Supabase, Firebase, and Firestore configs for exposure—then provides a single grade, report, and actionable fixes.
 Belgium
 EU


FlexNet Code Aware is a free code scanner that scans Java, NuGet and NPM packages looking for license compliance, IP, and security vulnerability risks.


Konvu automates vulnerability triage. It checks exploitability conditions against your code and environment, produces evidence-backed verdicts, and pushes results back to the tools you already use.


A single pane of glass for understanding and mitigating risks across your entire codebase and supply chain.
 United Kingdom


nittim scans a GitHub repository for committed secrets and vulnerable dependencies for free, then runs a full security audit that returns findings with evidence and a fix for each. It runs inside Cursor, Claude Code, Windsurf, Codex and Copilot through MCP, or from the web.


SecDash automatically detects security vulnerabilities in applications created with ChatGPT, Claude, and other AI tools, providing clear and actionable guidance.
 Brazil


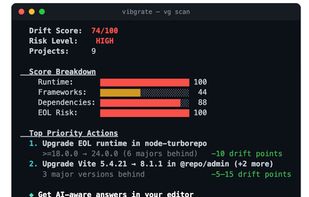
Local command-line scanner that measures dependency, framework and runtime drift, checks known vulnerability advisories, and prioritizes upgrades. It builds a code graph to trace imports and calls, assess change impact, and provide matching docs to AI assistants.
United Kingdom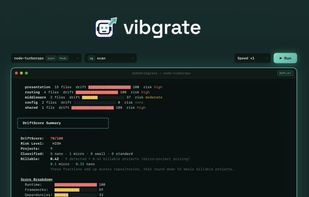


RankedRight is the triage tool that automatically ranks vulnerabilities based on the rules set by its user, factoring in what is critical to the business, and delegating it to the most appropriate person to resolve.
United Kingdom

sbomify is the trust center for your software supply chain. Store every SBOM and compliance document in one place, track them across products and releases, and share them with customers and regulators on demand. CycloneDX and SPDX, built for EU CRA compliance.
United Kingdom


Timesys Vigiles is a Software Composition Analysis (SCA) tool that helps generate and analyze a Software Bill of Materials (SBOM) for publicly known cybersecurity vulnerabilities, particularly CVEs. Vigiles is optimized for embedded systems, and it provides a complete...
United States


