




SignalVault
Like
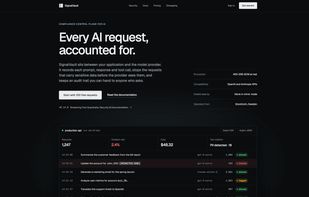
Proxy that logs every LLM prompt, response and tool call to an encrypted audit trail, and blocks or flags requests carrying PII, secrets or policy violations before they reach the provider.

Cost / License
- Freemium (Subscription)
- Proprietary
 EU
Platforms
- Online
- Software as a Service (SaaS)

Features


SignalVault News & Activities
Highlights All activities
Recent activities
- Mauricio B. Holguin updated SignalVault
- elliotjondev added SignalVault
 elliotjondev added SignalVault as alternative to Helicone, Langfuse, AcruxCore, AI Security Gateway and 2 more

SignalVault information
Developed by
 Elvar
Licensing
Proprietary and Freemium product.Pricing
Subscription ranging between $49 and $149 per month + free version with limited functionality.Alternatives
6 alternatives listedBadge
Get an embeddable badge for SignalVaultSupported Languages


No comments or reviews, maybe you want to be first?