


Scanner for vulnerabilities in container images, file systems, and Git repositories, as well as for configuration issues and hard-coded secrets.
Cost / License
- Free
- Open Source (Apache-2.0)
Application type
Platforms
- Mac
- Linux
- Docker
 Israel


Apps similar to CVE Lite CLI include Trivy, which is free and open source. Other options are Snyk, Dependabot, Retire.js and Patchdex. In total there are six Vulnerability Scanners like CVE Lite CLI for the web, Linux, Mac and Windows.
Scanner for vulnerabilities in container images, file systems, and Git repositories, as well as for configuration issues and hard-coded secrets.
Israel
 United Kingdom


Keep your dependencies on GitHub up to date without the automatic creation of the Pull Requests to update the dependency and checking for the known vulnerabilities.
https://github.blog/2020-06-01-keep-all-your-packages-up-to-date-with-dependabot/

The goal of Retire.js is to help you detect use of a JavaScript library version with known vulnerabilities.

Patchdex is a vulnerability database and package analysis tool. It provides instant security verdicts (RED, YELLOW, GREEN), checks for active malware, flags unpatched CVEs, and monitors maintainer health (abandonware, bus factor) to help developers choose safe dependencies.


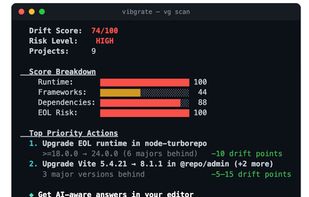
Local command-line scanner that measures dependency, framework and runtime drift, checks known vulnerability advisories, and prioritizes upgrades. It builds a code graph to trace imports and calls, assess change impact, and provide matching docs to AI assistants.
United Kingdom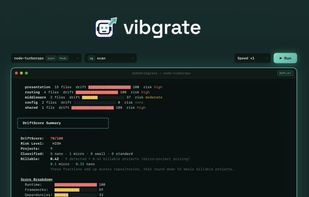


 United States

 Norway


