


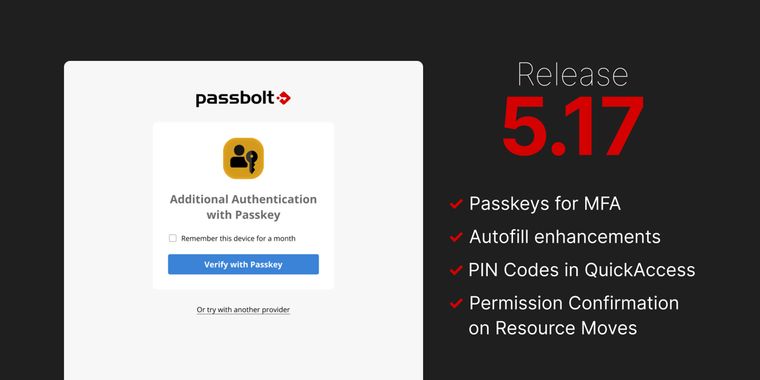

Passbolt 5.17 brings passkeys for MFA, autofill enhancements, and PIN codes in QuickAccess
Passbolt has released version 5.17, code-named “Mad World”, bringing passkeys to multifactor authentication and a ground-up rewrite of the browser extension's autofill detection engine. According to the company's changelog, passkeys join TOTP, YubiKey OTP and Duo as supported second factors, addressing what the release notes describe as a requirement many organizations now include in procurement processes: phishing-resistant multifactor authentication, which one-time codes alone cannot provide. The API additions also allow users to authenticate with passkeys from the Passbolt mobile app.
The autofill overhaul targets two long-standing complaints, per the changelog: missing autofill prompts on forms that plainly need credentials, and autofill icons appearing in fields unrelated to login data. Passbolt attributes the difficulty to the sheer variation between sites: differing field names, labels in many languages and inconsistent underlying markup meant the previous regex-based engine “had reached its limits”. Beyond autofill, the release makes permission changes easier to review when resources are moved, and brings PIN code resources into QuickAccess.
Administrative and security work rounds out the update. New API capabilities let administrators configure SCIM admin token expiry and a near-expiry window, with health check warnings and email notifications when tokens approach or pass expiration; admins can also clean up soft-deleted active resources that no longer have an associated secret, and a new “Is encrypted for its recipient” data check has been added to secrets. On the security side, the changelog lists fixes for blind SSRF via avatar upload, an MFA brute-force limiter that failed to count rejected TOTP codes sent to the JSON endpoint, and an SSRF egress guard bypass in SSO provider URL validation, along with patches for a high-severity braces vulnerability tracked as GHSA-vfj7-8cjw-p6xm. The browser extension also received a batch of dependency upgrades addressing multiple CVEs across libraries including axios, undici, shell-quote and fast-uri.


- Password Manager
- Freemium
- Open Source
Related news
External links
- Passbolt Release Note: 5.17.0 - Mad World | Browser Extension & APIPassbolt • Official source
- New release: 5.17.0 ~ "Mad World" | Browser Extension & APIPassbolt • Official source
No comments so far, maybe you want to be first?