Graylog is a powerful Security Information and Event Management (SIEM) solution offering a robust log analytics platform that simplifies the collection, search, analysis, and alerting of all types of machine-generated data.
United States
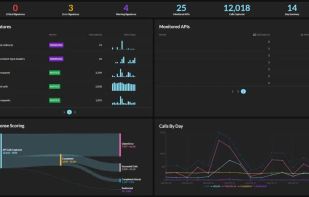


Graylog is a powerful Security Information and Event Management (SIEM) solution offering a robust log analytics platform that simplifies the collection, search, analysis, and alerting of all types of machine-generated data.


Cowrie is a medium interaction SSH and Telnet honeypot designed to log brute force attacks and the shell interaction performed by the attacker. Cowrie also functions as an SSH and telnet proxy to observe attacker behavior to another system.
AbuseIPDB is a project dedicated to helping combat the spread of hackers, spammers, and abusive activity on the internet.


Canaries can be deployed in minutes (even on complex networks), giving you all of the benefits of a honeypot without the admin downsides.

TypeFore is an operational integrity and compliance automation software solution that helps enterprise organizations audit, monitor, and safeguard internal communication data against regulatory and brand policy drift.


Gravwell is an all-you-can-ingest data fusion analytics platform that enables complete context and root cause analytics for security and business data.


Sift Security enables SOC, Incident Response and Threat Hunting teams to get their jobs done faster and with less frustration. Sift Security uniquely leverages AI and Graph Analytics to prioritize threats, accelerate investigations, and take action.


EventLog Analyzer collects, archives and displays huge amount of network logs (Syslog and SNMP trap) and help net and system admins in identifying security incidents, policy violations, and operational issues.


Our XDR (Extended Detection and Response) cyber security platform provides deep visibility and threat detection across your endpoints, servers, cloud and your digital supply chain. We deliver the platform to you as fully managed service supported by our 24×7 Security...


Get comprehensive identity protection with ExpressVPN’s Identity Defender: monitor, protect, and respond to threats—all from your VPN app.


Deception technology for early and accurate threat detection of in-network threats. Decoys, endpoint, application, and data deceptions deceive and detect attackers.
Kippo is a medium interaction SSH honeypot designed to log brute force attacks and, most importantly, the entire shell interaction performed by the attacker.
Free threat intelligence platform that aggregates 4000+ cybersecurity sources, clusters related articles, and delivers daily digests on APTs, ransomware, CVEs, and emerging threats.


Take control of external threats with NordStellar. Get alerts on dark web leaks and exposures to quickly detect where your business is most vulnerable.
Continuously identify vulnerabilities and simulate attack scenarios across your digital assets so you're always a step ahead.

Online brand protection powered by AI to combat phishing, fraud, counterfeiting & cyber threats. Ensure your brand remains secure.
Aves is a cloud-based cyber deception platform used to deploy and manage deception decoys in your on-premise & cloud environments.