


PrivacyAutomated.ai
Like
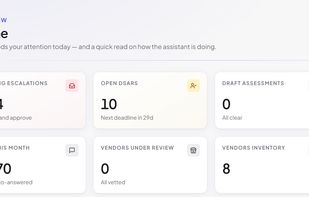
AI-powered privacy compliance for small teams — DSARs, DPIAs, RoPA, and vendor reviews, with regulator-verifiable audit trails.

Cost / License
- Freemium (Subscription)
- Proprietary
Platforms
- Software as a Service (SaaS)


Features
Highlights All activities
PrivacyAutomated.ai News & Activities
Recent activities
 NotSoLogical added PrivacyAutomated.ai as alternative to PrivBeacon
 Yann GUICHARD added PrivacyAutomated.ai as alternative to WebLegal.ai
 niango777 added PrivacyAutomated.ai as alternative to SetAIComply
 strakaje added PrivacyAutomated.ai as alternative to Termly.io
 strakaje added PrivacyAutomated.ai as alternative to Iubenda
- strakaje added PrivacyAutomated.ai
- strakaje added PrivacyAutomated.ai as alternative to OneTrust, Osano, Securiti, Transcend and 1 more


Developed by
 Privacy Automated
Licensing
Proprietary and Freemium product.Pricing
Subscription that costs up to $999 per month + free version with limited functionality.Alternatives
10 alternatives listedBadge
Get an embeddable badge for PrivacyAutomated.aiSupported Languages
No comments or reviews, maybe you want to be first?