Proactively detect advanced hacker activity earlier than ever. THOR’s impressive detection rate is well-known in the industry.
Cost / License
- Free
- Proprietary
Platforms
- Mac
- Windows
- Linux
- Online
- Software as a Service (SaaS)
 Germany
 EU


Apps similar to Nagios Log Server include Grafana, which is open source with a free version. Other options are Better Stack, Datadog, Graylog and Prometheus. There's no shortage of Web Log Analyzers like Nagios Log Server, with more than 50 alternatives for Windows, Linux, Mac, the web and self-hosting.
Proactively detect advanced hacker activity earlier than ever. THOR’s impressive detection rate is well-known in the industry.
GermanyEU
LogSentinel SIEM is a next-generation SIEM system offering simplicity and innovation. By leveraging the latest technologies like blockchain and AI, it helps companies of all sizes to reduce the time and cost of incident detection and investigation.
 Israel


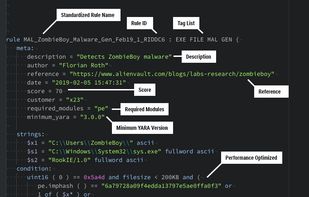
VALHALLA boosts your detection capabilities with the power of thousands of hand-crafted high-quality YARA and Sigma rules.
GermanyEU

Parseable is an open source, unified infrastructure observability platform built in Rust on a data lake architecture. It tracks logs, metrics, traces, and events across apps, agents, and systems.
 United States


DNIF provides a high value solution by combining technologies such as the SIEM, UEBA and SOAR into one product at an extremely low total cost of ownership.
 India


Fully managed enterprise class central logging service with queuing, indexing, searching and analysis features. On premise, hybrid and/or cloud based servers available for application, security systems and server event logging.
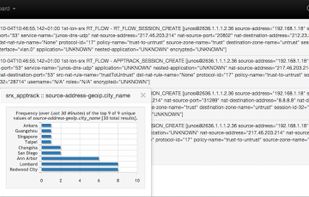


EventLog Analyzer, a log management software for SIEM, offers in-depth analytical capability to enhance network security with its predefined reports and real-time alerts. It also collects, monitors, correlates, and archives Windows event logs, syslogs, network devices logs...

A portable syslog server for Windows and macOS that displays multi-byte (Japanese, Chinese, Korean) log messages correctly, with per-message encoding detection. Single binary, no installation.
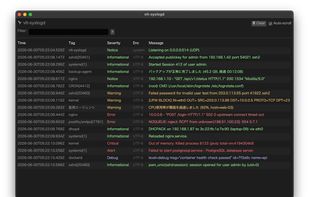


BLËSK is a suite of applications for network monitoring and management. All of the applications within BLËSK are finely tuned for the purpose having all your network monitoring applications running smoothly on a single machine.
 Canada


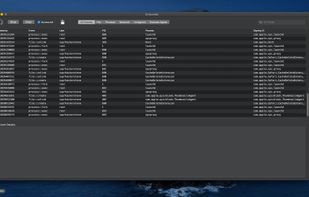
Crescendo is a real time event viewer for macOS that uses the ESF to show process executions and forks, file events, share mounting events, kernel extension loads, and IPC event data. ESF provides a vast amount of data, but the goal was to just pick out the things that analysts...


Syslog Watcher is a dedicated syslog server, integrating log data from multiple network devices into a single, easily manageable and accessible place.