


Searches through git repositories for secrets, digging deep into commit history and branches. This is effective at finding secrets accidentally committed.
Cost / License
- Free
- Open Source (AGPL-3.0)
Since
- Since 2019




Sites and apps similar to Guardlayer include SonarQube, which is open source with a free version. Other options are Codacy, Artemis Security Scanner, VibeGuard and Aikido Security. Vulnerability Scanners like Guardlayer are a crowded field, with more than 25 alternatives for Windows, Linux, Mac and self-hosting.
Searches through git repositories for secrets, digging deep into commit history and branches. This is effective at finding secrets accidentally committed.

Mend Bolt is designed to provide real-time security alerts and compliance issues related to your open source dependencies. It operates within Azure DevOps or GitHub, enabling you to identify and address open source vulnerabilities promptly.
 Israel


vibecheck is a security scanner for GitHub repositories built by developers who use AI coding assistants. It runs four real static analysis tools — Gitleaks, Semgrep, njsscan, and custom checks — against your codebase, then uses Claude AI to explain the findings in plain...
 United Kingdom


Find and fix bug risks, anti-patterns, performance issues, security flaws automatically during code reviews. In addition, DeepSource automatically fixes some of the most commonly occurring issues. It works for Python, Go, Ruby, and JavaScript.


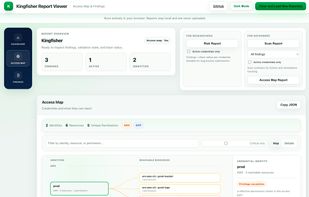
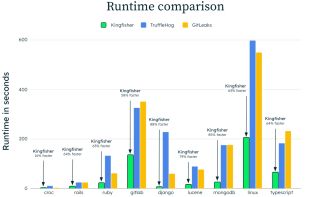
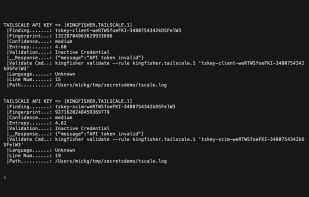
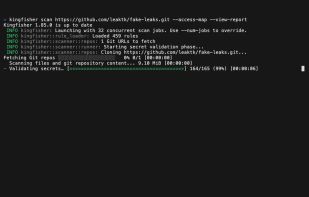
Kingfisher is a high-speed, open-source secret scanner and live validation tool. It scans code, Git history, developer platforms, cloud storage, collaboration tools, and containers, then verifies exposed credentials, maps their blast radius across identities, permissions, and...
 United States

Mend.io offers the first AI native application security platform, purpose-built to secure AI-generated code and embedded AI components. Our unified platform enables companies to manage application risk effectively in modern software development.
Israel


AquilaX Ultimate is a comprehensive software security scanner, designed to detect a wide range of security vulnerabilities in the source code of any application. Is committed to change how contextual analysis is done to eliminate virtually any false positive.
United Kingdom


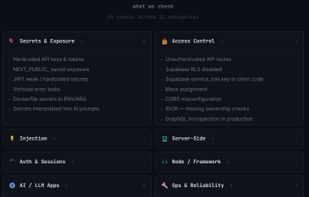
Examines codebases for secrets, dependency risks, and unsafe API keys, checks running apps for TLS and security headers, and analyzes Supabase, Firebase, and Firestore configs for exposure—then provides a single grade, report, and actionable fixes.
 Belgium
 EU


Vibe coding gets you from idea to live app in hours, but the security review is usually the first thing that gets skipped. Decloak is built to catch what shipping fast leaves behind.
United Kingdom
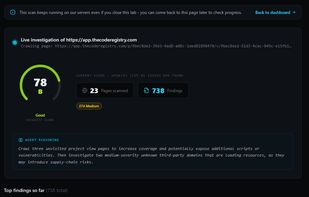
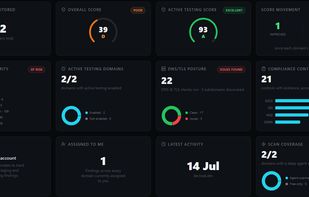
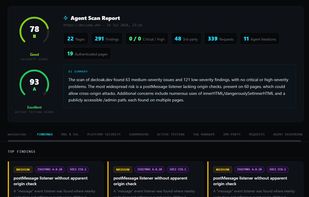


SecDash automatically detects security vulnerabilities in applications created with ChatGPT, Claude, and other AI tools, providing clear and actionable guidance.
 Brazil


GuardRails continuously scans your GitHub & GitLab repositories to alert you of any vulnerabilities and security issues. Get started in minutes.

ScanMyApp is an AI agent that audits the code of web apps for security flaws. The free scan checks what your live app exposes publicly: leaked API keys, missing security headers, HTTPS issues and exposed files. The full audit connects to your GitHub repo with read-only access.


 Singapore


