




Droynis
Like
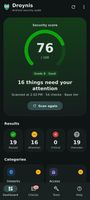
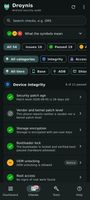
Offline Android security audit tool. 63 read-only checks across multiple privilege levels (base, ADB, Shizuku, root), 0–100 score and saved reports. Privacy-oriented, no internet permission, zero telemetry, fully local.


+1

 EU
Platforms
- Android
- F-Droid
Add Alternatives

0likes
0alternatives
0articles
Features
Highlights All activities
Droynis News & Activities
Recent activities
Developed by
 capitan0n
Licensing
Open Source (GPL-3.0) and Free product.Alternatives
0 alternatives listedBadge
Get an embeddable badge for DroynisSupported Languages
AlternativeTo Categories
Security & Privacy, Network & AdminGitHub repository
- 10 Stars
- 1 Forks
- 0 Open Issues
- Updated
No comments or reviews, maybe you want to be first?