




BoringSec
Like
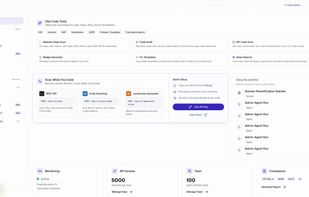
BoringSec is an application security platform for developers, founders, product teams, and agencies. It combines code review, live application scanning, evidence-backed findings, AI-ready remediation, re-testing, and continuous monitoring in one workflow.

Cost / License
- Freemium (Pay once or Subscription)
- Proprietary
Application typeApplication types
 EU
Platforms
- Online
- Software as a Service (SaaS)


Features
BoringSec News & Activities
Highlights All activities
Recent activities

BoringSec information
Developed by
 Orbitwise LTD
Licensing
Proprietary and Freemium product.Pricing
One time purchase that costs $56, and / or subscription ranging between $33 and $283 per month + free version with limited functionality.Alternatives
5 alternatives listedBadge
Get an embeddable badge for BoringSecSupported Languages


No comments or reviews, maybe you want to be first?