


Mbox is a lightweight sandboxing mechanism that any user can use without special privileges in commodity operating systems.
Cost / License
- Free
- Open Source
Alerts
- Discontinued
Platforms
- Linux


Sites and apps similar to ANY.RUN include VirusTotal, which is free for personal use. Other options are SpiderFoot, Hybrid-Analysis.com, Cuckoo Sandbox and Firejail. You're spoiled for choice with Anti-Malware Apps like ANY.RUN: we list more than 25 alternatives for Linux, Windows, Mac, Android and self-hosting.
Mbox is a lightweight sandboxing mechanism that any user can use without special privileges in commodity operating systems.

Submit your file or URL, get back reports from a full analysis using SophosLabs Intelix. Find out what our machine learning, decades of threat research, and petabytes of intelligence will say about your sample.
 United Kingdom


IObit Cloud is an advanced automated threat analysis system. We use the latest cloud computing technology and heuristic analyzing mechanic to analyze the behavior of spyware, adware, trojans, keyloggers, bots, worms, hijackers and other security-related risks in a fully...
 China


Online scan of files (size should be less than 10MB) and links by Dr.Web Security Space
 Russia


Cisco Talos's PyREbox is a python QEMU-based sandbox environment designed to aid in reverse engineering. It can be used for security researchers to aid them in malware analysis, or for general developers with debugging their applications.


REVERSS can analyze executables, URLs and PCAP files. It also show statistical data about found infections and the affected countries, etc. You can send the samples anonymously or logged in with Google to scan it privately.

Automated malware analysis sandbox that detonates files, URLs, documents and Windows kernel drivers in isolated virtual machines and returns a scored verdict.
 Türkiye
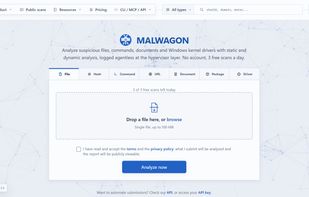
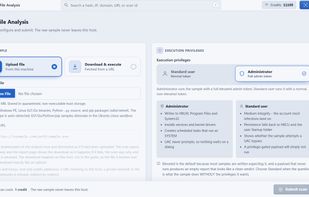
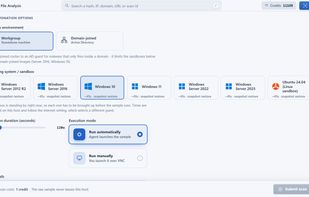


 Israel


Isolate programs and coding agents without leaving your familiar work environment.
 Poland
 EU


UNPACME is an automated malware unpacking service. Submissions to UNPACME are analyzed using a set of custom unpacking and artifact extraction processes. These processes extract all encrypted or packed payloads from the submission and return a unique set of payloads to the user.
 Canada


urlDNA is a comprehensive web analysis tool designed to provide detailed insights into websites. It features information extraction (such as screenshots, IP information, and favicons), brand monitoring, database searches, and website safety evaluation, making it ideal for...


CAPE is a malware sandbox. It was derived from Cuckoo with the goal of adding automated malware unpacking and config extraction.
United Kingdom


 United States


