Airbrake collects errors generated by other applications, and aggregates the results for review.
Cost / License
- Paid
- Proprietary
Since
- Since 2010
Platforms
- Online
- Ruby on Rails
 United States


One of the most popular alternatives to Graylog is Better Stack, which is free for personal use. Other popular alternatives are Datadog, Kibana, Wazuh and Splunk. Web Log Analyzers like Graylog are a crowded field, with more than 50 alternatives for the web, Linux, Windows, Mac and self-hosting.
Airbrake collects errors generated by other applications, and aggregates the results for review.
United States
Grafana Tempo is an open-source, easy-to-use, and high-scale distributed tracing backend. Tempo lets you search for traces, generate metrics from spans, and link your tracing data with logs and metrics.
 Sweden
 EU


SigLens is a cutting-edge, purpose-built solution designed to efficiently manage massive volumes of data ranging from terabytes to petabytes, all while optimizing resource utilization. Functioning as a column-oriented database, SigLens incorporates dynamic columnar compressions...


Monitor actual user JavaScript errors as they happen. JSMonitor features real-time alerts, prioritization, and tracking features to squash JavaScript errors forever.


BLËSK is a suite of applications for network monitoring and management. All of the applications within BLËSK are finely tuned for the purpose having all your network monitoring applications running smoothly on a single machine.
 Canada


Nerdlog is a fast, remote-first, multi-host TUI log viewer with timeline histogram and no central server. Loosely inspired by Graylog/Kibana, but without the bloat. Pretty much no setup needed, either.


A cloud-native observability platform built specifically for logs, metrics, traces, analytics, RUM (real user monitoring — performance, errors, session replay) designed to work at petabyte scale.
United States


Virtual-appliance log platform for on-network deployment, ingesting OTLP, syslog, and Fluentd data. It pairs natural-language log search and alert root-cause analysis with an LLM endpoint you control, while retaining search, dashboards, alerting, and incident tracking.
 India

LogPulse is an AI-assisted, Kubernetes-native log management platform for engineering and platform teams. Search logs in natural language or with LPQL, a Splunk-familiar pipe-based query language (30+ commands like stats, timechart, eval and lookup), and investigate incidents...
 NetherlandsEU
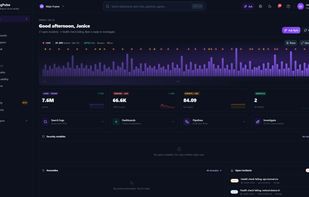


A simple and lightweight tool that allows you to capture logs from your applications and monitor them in one easy dashboard.
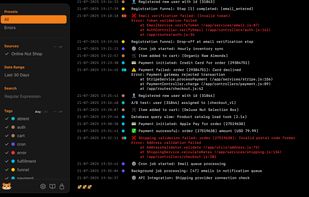

Open-source, self-hosted platform for logs and OpenTelemetry traces, with full-text search running on S3-compatible object storage.
 PolandEU

Parseable is an open source, unified infrastructure observability platform built in Rust on a data lake architecture. It tracks logs, metrics, traces, and events across apps, agents, and systems.
United States